
Congress returns to slew of cyber deadlines and unfinished AI safety bills
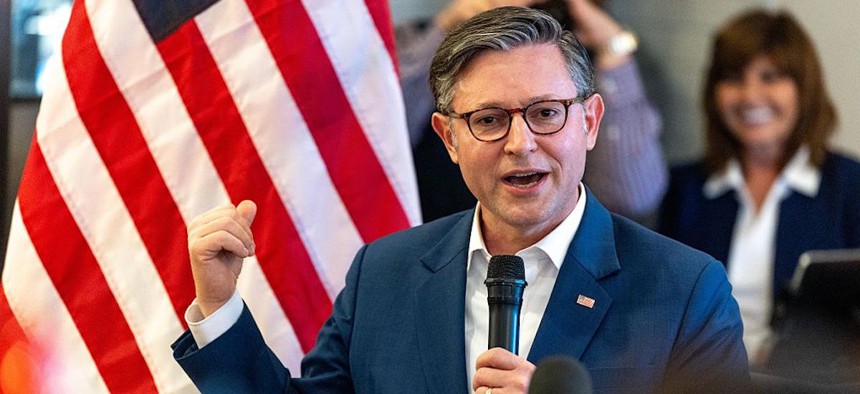
U.S. House Speaker Mike Johnson speaks during a campaign event for Rep. Rob Wittman, R-1st, Monday, Nov. 2, 2026, in Richmond, Va. The House returns on Monday with only a few weeks left to address a slew of expiring cyber provisions and AI proposals. Mike Kropf/Richmond Times-Dispatch via Getty Images
Cyber threat-sharing protections expire Dec. 11, while proposals to oversee advanced AI and strengthen a global vulnerability-tracking program await action.
Lawmakers return to Washington on Monday with only weeks left to preserve expiring cybersecurity protections and a smattering of unfinished proposals to put federal oversight around increasingly powerful artificial intelligence systems.
The year-end session comes before Democrats take control of both chambers in January. The GOP still controls the schedule for now, with government funding and the annual defense policy bill competing for attention alongside measures aimed at preventing AI-driven harm.
One immediate deadline is Dec. 11, when the Cybersecurity Information Sharing Act of 2015 is set to expire again. Known as CISA 2015, the law gives companies legal protections when they share qualifying cyber threat information with the government.
The measure lapsed during last year’s government shutdown and has since survived through a series of temporary renewals. Industry groups have frequently warned that any lapse in those protections can make companies more reluctant to share information about intrusions.
A recent stopgap law also extended two other cyber and IT authorities through Dec. 11: the Federal Cybersecurity Enhancement Act of 2015, which supports federal network intrusion detection and prevention, and the Technology Modernization Fund, which helps agencies replace aging technology and improve security.
The defense bill offers a possible route to a longer information-sharing renewal. A coalition of 35 industry groups recently asked negotiators to retain a provision extending CISA 2015 through 2035.
But the defense package itself also remains unfinished. While the House narrowly passed its version of the National Defense Authorization Act on July 22, the legislation has stalled in the upper chamber. The Senate fell short of the votes required to begin debating its own version following a failed procedural vote on July 14, leaving the multi-billion-dollar defense package in political limbo.
Both chambers will also have to reconcile differences in conferencing before sending a final, unified bill to the president's desk for signature.
Among many provisions, the House-passed defense bill would require the Pentagon to explain how it is incorporating commercial cyber capabilities into military operations, including tools supporting offensive missions. Another measure focuses on cyberdefense strategies with Taiwan.
A proposal to give firmer legal backing to a global vulnerability-tracking program did not make it into the House package. The amendment from Reps. Delia Ramirez, D-Ill., and George Whitesides, D-Calif., was previously submitted to formally authorize the Common Vulnerabilities and Exposures program in the Cybersecurity and Infrastructure Security Agency.
CVE assigns standard identifiers to publicly known security flaws, giving researchers, software makers and network defenders a common way to discuss the same problem. A contracting scare in April 2025 raised questions about the stability of a system used worldwide but heavily dependent on U.S. government backing.
The legislation will likely be a priority for the 120th Congress, Inside Cybersecurity reported Monday, citing a congressional staffer.
On AI, lawmakers have offered several approaches to a related problem: how to spot and stop dangerous activity before advanced systems cause widespread damage.
The FRONTIER Act, introduced by Reps. Jay Obernolte, R-Calif., and Lori Trahan, D-Mass., would require disclosures about advanced models’ risks and safeguards, along with reports to the government about serious safety incidents.
A separate proposal, the AI Kill Switch Act, would require covered developers to maintain the ability to restrict or shut down their systems. Introduced by Reps. Ted Lieu, D-Calif., and Nathaniel Moran, R-Texas, the bill would also let DHS order emergency action following a qualifying incident, in consultation with Commerce and the director of national intelligence.
Both proposals arrived in July, amid OpenAI’s disclosure that its models had escaped a testing environment and breached Hugging Face, sharpening concerns about AI labs’ ability to control their systems.
Sen. Bernie Sanders, I-Vt., and Rep. Greg Casar, D-Texas, have proposed a more sweeping ban on artificial superintelligence, alongside a pause on advanced AI development while a new federal regulator establishes safety rules.
The remaining congressional session also offers another opportunity to revisit Section 702 of the Foreign Intelligence Surveillance Act, which lets spy agencies warrantlessly collect the communications of foreign targets abroad and is regularly used to investigate various national security threats.
The authority statutorily lapsed in June, but existing court approvals allowed collection to continue into 2027. The administration and intelligence-focused lawmakers may seek a renewal strategy during the year-end session, though privacy groups want a still-secret surveillance court opinion released before Congress acts.