International
US order to purge Acronis tied to years of scrutiny over Russian ties
Sources say federal oversight of the Swiss cybersecurity firm spanned multiple administrations before culminating in last week's DHS removal order.
Updated
FBI links $6.3 billion Binance hack to North Korea
Researchers say the hack is the largest cryptocurrency theft on record, raising concerns about North Korea’s ability to finance its government and weapons programs.
US signs emerging technology deal with Finland
The deal advances the countries’ cooperation on technologies like artificial intelligence and quantum computing.
Pentagon investigates suspected cyberattack behind military freezer failures
August outages spoiled food at military commissaries across the nation. Investigators are also examining a similar attack on refrigeration systems in France.
China’s ‘Volt Typhoon’ quietly built another hacking network following US crackdown, new findings say
New research traces a three-year operation targeting government, defense and critical infrastructure networks. Sources say Energy Department facilities and utilities have also been affected.
Transportation turns to AI to trace research grant recipients’ links to foreign adversaries
Neil Chaudhry, senior advisor for AI at Transportation, says the agency has worked with its partners to create “some really robust AI tools” to analyze the recipients of its research grants.
OpenAI bugging case highlights AI’s insider threat problem
Researchers say the alleged recording attempt shows why AI companies need tighter controls on employee access to sensitive information.
Officials see gaps in election communications as AI makes foreign influence easier
Sources describe weakening cooperation between the federal government and state and industry partners ahead of the midterms, as AI gives foreign operatives cheaper ways to produce and spread deceptive messages.
FBI disrupts North Korean ‘laptop farm’ used to infiltrate US companies
Agents seized nearly 190 laptops across Texas in a crackdown on fraudulent remote workers whose earnings help fund Pyongyang’s weapons programs.
GSA removes 244 Chinese products from procurement list
The agency is seeking to fulfill ‘truthful advertising’ and fraud-busting executive orders signed by President Donald Trump.
FBI seizes websites supporting Chinese contractor’s hacking operations
U.S. agencies targeted tools used to find security weaknesses and break into networks, warning of threats to critical infrastructure.
Recent Taiwan simulation highlights US cyberdefense gaps against China, experts warn
Organizers of a cyber conflict exercise say Washington needs to prepare for attacks that both disrupt civilian services and pressure Taipei without triggering outright military conflict.
China-linked hackers posed as former US officials, Anthropic employee to target AI experts
Proofpoint identified phishing campaigns that borrowed prominent figures’ identities to approach U.S. policy researchers before attempting to steal access to their cloud accounts.
Senators propose voluntary telecom security framework after Salt Typhoon hacks
The bipartisan bill would establish cybersecurity best practices and independent certification, following the FCC’s rollback of safeguards adopted in response to the Chinese hacking campaign.


25 years after 9/11, spy agencies face old lessons and new threats
Former intelligence officials describe a nation better equipped to disrupt terrorist plots, but still wrestling with the costs of its response and how to prevent the next crisis under escalating technology threats.
Lawmakers ask Commerce to sanction Indian firms involved in mercenary hacking
The “hack-for-hire” entities have systematically targeted newsrooms covering corporate fraud, legal teams in high-stakes litigation and NGOs.
Intelligence agencies warn of China’s large-scale AI model distillation efforts
Three agencies issued a joint statement warning that Chinese companies DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun and Z.AI have used the tactics to extract billions of tokens from U.S. models.
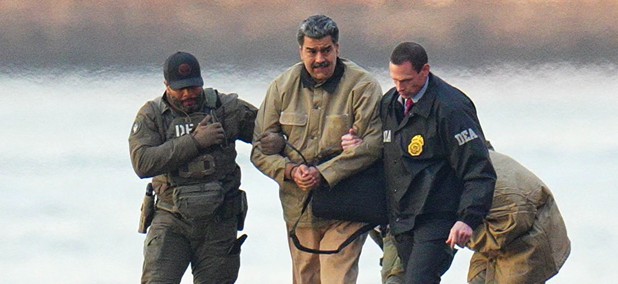
CIA cyber intelligence helped US forces capture Maduro, deputy director says
Michael Ellis credited the agency’s cyber intelligence officers with helping U.S. troops locate and apprehend the Venezuelan leader within minutes of landing.
Trump admin moves to block risky foreign technology from US power grid
A new executive order targets hardware, software and remote-access services and could require operators to isolate or replace equipment already in use.
FBI disables China-linked hacking tools used against US agencies
A hacking group used the tools to target networks belonging to NASA, the Federal Reserve, the National Institutes of Health, the U.S. Senate and the departments of Energy, Justice and Health and Human Services.
