Ransomware


FBI Cyber Division deputy director departs for anti-ransomware firm
Cynthia Kaiser will serve as senior vice president for Halcyon’s Ransomware Research Center.


US charges Israeli-Russian national with making software for LockBit ransomware gang
LockBit has made headlines for years, allowing purveyors of its malware to haul away millions of dollars from victims.


Under a quarter of rural hospitals are using White House’s free cyber resource program, official says
The commitments from industry leaders announced in June seek to help small healthcare centers boost their cybersecurity posture.


FBI, Mandiant designate advanced North Korean hackers stealing US defense secrets
The group — now known as APT45 — has targeted information stored in U.S. government nuclear facilities and research institutions, as well as missile systems, uranium processing and other R&D intel.
Ransomware payment debate resurfaces amid Change Healthcare incident
Expert views don’t entirely align on whether victims should pay ransomware hackers.
Government facilities were third largest ransomware target in 2023, FBI says
The FBI’s IC3 findings also show government official impersonation scams are on the rise.
US, international partners disrupt LockBit ransomware operations
Officials have also developed a tool for victims targeted by LockBit to potentially decrypt their compromised data.
US must ratchet up its response in pursuing hackers, MITRE CTO argues
The technical and innovation strategy leader sat down with Nextgov/FCW to discuss recent events in cyberspace and the government’s response to bad actors.
CISA, FBI warn of social engineering-based ransomware
Federal agencies are revealing more information on the Scattered Spider cybercriminal group in a bid to both prevent breaches and encourage victims to offer more detail on such attacks.
How the US aims to tackle the ‘collective action problem’ of ransomware
New efforts in the International Counter Ransomware Initiative intend to leverage automated systems to halt illicit financial transactions, according to a White House cyber official.
Ransomware group's evolving tactics pose growing threat
A joint advisory from the FBI and the nation’s cyber defense agency warns that a persistent threat actor is advancing its tactics and targeting critical infrastructure sectors.
Cyber Agencies Unveil Updated Ransomware Guide
The 2023 version offers more detailed, step-by-step guidance and associated recommendations to fortify public and private networks against sophisticated ransomware.
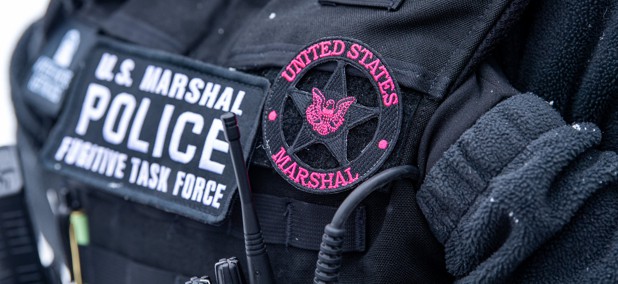
US Marshals to Unveil ‘Fully Reconstituted System’ Following Ransomware Attack
Offline since February, the new system will have improved cybersecurity countermeasures.
Biden Admin to Debut New Emerging Tech Policies at Summit for Democracy
The virtual conference will spotlight how to marry emerging technologies with democratic values, and the U.S. will spearhead new initiatives domestically and abroad.
CISA Launches Ransomware Warning Pilot for Critical Infrastructure
The new pilot program will enable “timely risk reduction” by alerting critical infrastructure owners and operators of vulnerabilities within their systems that are susceptible to ransomware attacks.
Ransomware Payments Decreased in 2022 as Criminals Used Other Extortion Tactics
A report from Recorded Future found that, even as ransomware continues to pose a global challenge for individuals and organizations, threat actors are increasingly using other methods to steal sensitive data and demand payments from victims.
A CISA Test Hack Offers Warnings for Critical Infrastructure Organizations
A CISA red team simulated a malicious cyberattack on a critical infrastructure organization to test security measures and give recommendations to other entities.
Report Reveals How US Has 'Not Advanced the Ball' on Top Cyber Risks
The top cybersecurity risks of 2023 include a shortage of trained cyber professionals, international strife and continued vulnerabilities in critical infrastructure services, according to a new report from the Bipartisan Policy Center.
CISA, South Korean Agencies Issue Joint Warning on North Korean Ransomware
The new cybersecurity advisory spotlights North Korean-backed actors targeting healthcare networks with ransomware.
US and UK Join Forces to Sanction Russian Hackers
Members of cybercrime group Trickbot, which favors deploying ransomware on critical infrastructure, were handed sanctions in the first-of-its-kind collaboration between U.S. and U.K. agencies.
