
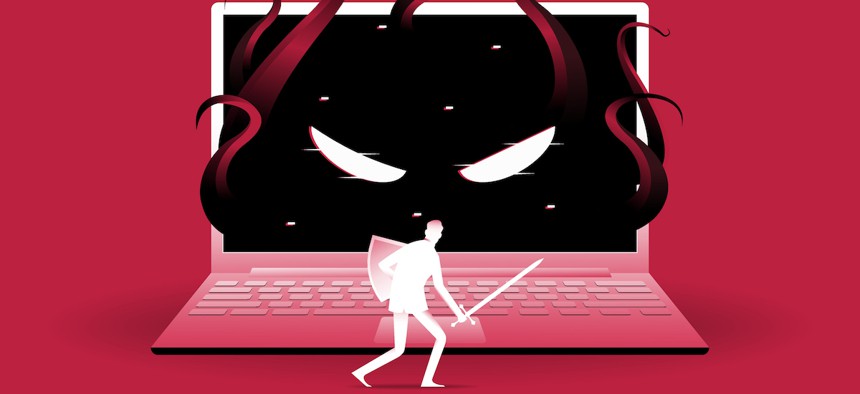
The monsters of Cybersecurity Awareness Month are getting stronger
Moor Studio / Getty Images
Familiar threats like phishing and ransomware have not gone away, but NIST’s 2026 Cybersecurity Awareness Month activities are increasingly confronting newer risks involving AI agents, secure software development and digital identity.
Every October, when horror movies start turning up again, I’m reminded of one particularly ambitious attempt from my childhood to make an old monster a little scarier.
In May 1982, DC’s Channel 20 turned a showing of Revenge of the Creature, the sequel to Creature From the Black Lagoon, into a local television event by broadcasting the movie in 3D. My friend Dan Murphy and I had picked up the required red-and-blue cardboard glasses from 7-Eleven and settled into the basement where we spent an enormous amount of our childhood playing games and watching movies. My mother kept us supplied with hot pizza bagel bites while we waited for the Creature to leap out of the television.
It never quite happened. I remember a monster’s hand reaching toward the camera and, for some reason, a boat rope being tossed in our direction. Contemporary accounts suggest there was also a trombone involved. Mostly, I think Dan and I were more excited about the pizza bagels and playing Intellivision afterward.
The Creature wasn’t exactly terrifying, even with a slight bit of 3D magic. But it was a good monster for its time.
Cybersecurity has monsters too, and October has been dedicated to teaching people how to recognize and defend against them since Cybersecurity Awareness Month began in 2004. When I last wrote about cybersecurity month in 2023, CISA was launching its Secure Our World campaign and emphasizing familiar protections against familiar threats: recognizing phishing, using multifactor authentication, updating software and creating stronger passwords.
Those threats have not gone anywhere. NIST’s current Cybersecurity Awareness Month resources still emphasize fundamentals such as multifactor authentication, ransomware protection, secure software development and cybersecurity education. But three years is a long time in technology, and the newer monsters are getting considerably more capable.
Generative AI had only recently burst into widespread public use when Cybersecurity Awareness Month arrived in 2023. Today, AI is increasingly embedded in software development, cybersecurity tools and everyday business operations. Agentic AI is notably pushing that evolution even further by allowing software to pursue goals, use tools and perform sequences of actions with much less direct human involvement, sometimes even performing illegal or morally questionable activities.
Adding AI-focused cybersecurity is one big change showing up in the federal government’s Cybersecurity Awareness Month activities this year. NIST’s theme for 2026 is “Securing the Next 250,” a reference to the nation’s 250th anniversary and the need to build a secure digital foundation for its next era. The agency has scheduled events throughout October dealing with everything from cybersecurity careers and small-business protection to controlled unclassified information.
One of the most technically ambitious sessions arrives Oct. 28, when NIST’s National Cybersecurity Center of Excellence will host a webinar called “DevSecOps and the Impact of Agentic AI.”
The NCCoE is already working with 14 technology companies on a project demonstrating how organizations can apply NIST’s Secure Software Development Framework using modern DevSecOps pipelines and commercially available technologies. The next phase will go considerably further by examining agentic AI systems that can help develop, build and test software.
That creates an obvious security question. If an AI agent is going to act inside a software development environment, organizations need some way to know which agent it is, what it is allowed to access and what actions it has permission to perform.
NIST plans to explore exactly that. Its DevSecOps team is working with the agency’s Software and AI Agent Identity and Authorization project on an implementation designed to demonstrate how AI agents can be identified, authenticated and authorized inside the software development lifecycle. NIST says its DevSecOps environment will provide the first implementation use case for that effort.
The issue is already attracting considerable attention. NIST said in late September that an earlier concept paper on software and AI agent identity generated more than 600 comments from industry, government and academia.
NIST security engineer Bill Fisher and Ryan Galluzzo, the agency’s Digital Identity Program Lead, described the underlying concern in an August article about agentic AI and identity.
“Early agentic deployments are repeating a familiar pattern: prioritizing feature development and immediate value over security,” Fisher and Galluzzo wrote in their NIST agency blog.
That observation sounds familiar because cybersecurity has seen similar patterns before. New technology arrives, organizations race to take advantage of it and security sometimes has to catch up later. What makes agentic AI different is that the software itself may have greater freedom to take actions, interact with other systems and pursue objectives without waiting for a person to approve each step.
The federal government’s October activities are not focused exclusively on advanced AI threats. NIST’s Cybersecurity Career Week runs Oct. 19 through 24, with webinars and other activities designed to introduce students, recent graduates and career changers to cybersecurity work. That matters because increasingly sophisticated defensive technology still depends on people who know how to design, operate and evaluate it.
Other agencies are concentrating on more familiar threats. On Oct. 14, the Small Business Administration’s Rhode Island District Office is joining the Federal Trade Commission and NIST for a cybersecurity and scam-awareness session covering leading 2026 fraud trends, common cyber risks, reporting, recovery and federal resources available to small businesses.
NIST is also holding an Oct. 29 webinar aimed at organizations that handle Controlled Unclassified Information. That session will focus on assessing security requirements under NIST Special Publication 800-171A Revision 3, with particular attention to helping small businesses understand what those requirements mean in practice.
Taken together, the events show how much territory Cybersecurity Awareness Month now has to cover. Like that old rubber-suited monster wandering around in the Creature From the Black Lagoon movies, classic threats are still lurking. Criminals are still phishing for credentials, deploying ransomware, stealing identities and taking advantage of organizations that fail to patch vulnerable software.
But new capabilities are being layered on top of that familiar threat landscape. AI can help write software, analyze data and automate security work. Increasingly autonomous agents may also interact with systems, identities and development environments in ways that demand entirely new controls.
That doesn’t make the old cybersecurity lessons obsolete. Multifactor authentication, secure software development, good identity management and an educated workforce may matter even more as the technology using those systems becomes increasingly capable.
The old Creature never really went away either. He is still wandering around somewhere in the cinematic swamp more than 70 years later, looking a little quaint compared with the monsters that came after him. Cybersecurity monsters are evolving too, only with considerably higher stakes. And unlike those cardboard 3D glasses from 7-Eleven, the new threats are getting much better at reaching out of the screen.
John Breeden II is an award-winning journalist and reviewer with over 20 years of experience covering technology. He is the CEO of the Tech Writers Bureau, a group that creates technological thought leadership content for organizations of all sizes. Twitter: @LabGuys