
CISA updates cyber reporting form as broader incident mandate awaits approval
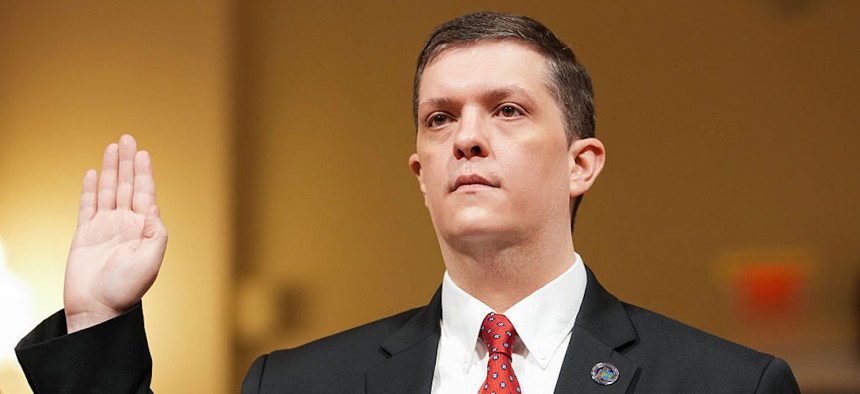
Cybersecurity and Infrastructure Security Agency (CISA) Acting Director and Deputy Director Nicholas Andersen is sworn in during a House Homeland Security Committee hearing on Capitol Hill on March 25, 2026 in Washington, DC. Andrew Harnik/Getty Images
The agency wants more thorough details about cyberattacks while its long-delayed CIRCIA rulemaking remains under review.
The Cybersecurity and Infrastructure Security Agency updated its cyber incident reporting form on Monday, aiming to gather more detail about attacks and help connect incidents that might otherwise appear unrelated.
The revised questionnaire, available through CISA’s Incident Reporting Portal, asks more specific questions about malicious software, hacking techniques, insider threats and efforts to trick people into giving cyber intruders access to systems. CISA said it also removed duplicate questions and implemented feedback from incident response partners.
The update comes as the agency works to complete a much broader requirement for critical infrastructure organizations to disclose significant attacks. That final rule, which implements the Cyber Incident Reporting for Critical Infrastructure Act — or CIRCIA — reached White House review on Oct. 1 and remains listed as pending.
The form now incorporates MITRE’s “ATT&CK” framework, a widely used catalog of attacker behavior. Common descriptions of what hackers carry out in their operations can help analysts compare incidents across different organizations and identify who may be responsible.
“As the national coordinator for critical infrastructure cybersecurity and resilience, CISA is able to leverage such incident reporting to identify emerging cyber campaigns, warn potential targets, and strengthen the Nation’s collective defense,” Chris Butera, CISA’s acting executive assistant director for cybersecurity, said in a statement.
Congress passed CIRCIA in 2022 following major attacks, including the SolarWinds espionage campaign and the Colonial Pipeline ransomware incident, that exposed gaps in the government’s knowledge of breaches affecting critical services.
Once implementing regulations take effect, organizations will have to report substantial cyber incidents within 72 hours of reasonably believing they occurred and ransom payments within 24 hours of making them. The reports are intended to help CISA assist victims and warn others before hackers can repeat the same methods elsewhere.
The CIRCIA rules have taken years to develop. CISA published its proposal in April 2024 and missed an October 2025 statutory deadline to finalize it. The agency later targeted September 2026, after a DHS funding lapse delayed additional industry meetings until June.
Companies have mostly pushed back on the scope of the mandate, citing the fact that they have to meet additional cybersecurity incident reporting requirements set by other federal agencies who oversee sectors like banking and telecommunications.