
CISA outlines internal plan to swiftly address cyber, infrastructure threats
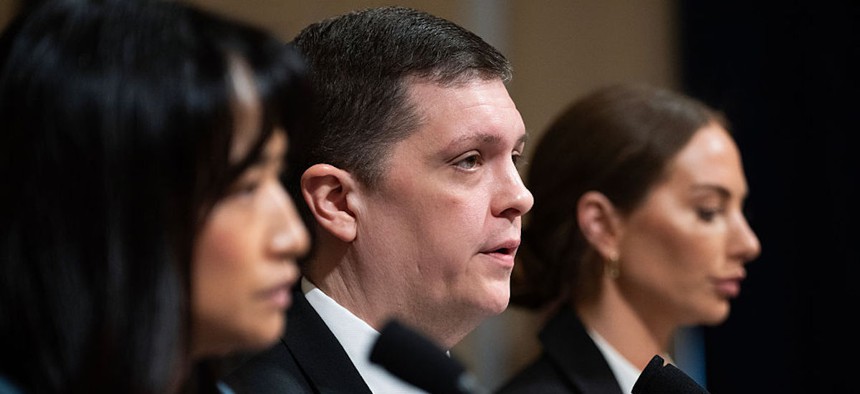
Nick Andersen, acting director of the Cybersecurity and Infrastructure Security Agency, testifies during a House Homeland Security Committee hearing in Washington, D.C., on Wednesday, March 25, 2026. Ha Nguyen McNeill, left, acting Transportation Security Administration administrator, and Victoria Barton, Associate Administrator, Office of External Affairs, FEMA, also appeared before the panel. Tom Williams/CQ-Roll Call, Inc via Getty Images
Guidance to agency staff outlines what senior officials need to know about major risks, national preparedness and CISA’s ability to respond, using terminology familiar in military and intelligence planning.
The Cybersecurity and Infrastructure Security Agency circulated an internal framework last week intended to help senior officials assess major cybersecurity threats and act before they could potentially escalate into a crisis, according to an internal email viewed by Nextgov/FCW.
The Nov. 5 email, which is unclassified but marked “For Official Use Only,” was sent to staff by acting Director Nick Andersen. It outlines what agency leaders need to know to assess risks and make timely decisions, aiming to help officials “cut through the noise” and distinguish useful information from what is mission-critical.
The framework sets out six “operational focus areas” that include priorities assessing national risk, defending against major cyber threats, preparing for serious incidents, helping critical infrastructure withstand disruptions and coordinating with partners.
Its “critical information requirements” spell out what senior officials need to know to make decisions. Those include major changes in risk, serious threats and incidents and impacts on nationally significant infrastructure. They also cover how prepared the country is, how efforts are coordinated and whether CISA has the capacity to carry out its mission.
A separate set of “priority intelligence requirements” identifies questions that intelligence work can help answer. These include how changing conditions affect critical infrastructure, what warning signs could point to serious risks and where and how hackers are operating against U.S. and allied computer networks and industrial systems. Those questions also cover how cyber and physical risks are managed, along with supply chains and production capabilities.
Such terminology has had longstanding uses in military and intelligence planning. Priority intelligence requirements, or PIRs, help focus intelligence collection and analysis on the questions leaders consider most important. Military commanders also establish commander’s critical information requirements, or CCIRs, to identify information essential to timely decisions.
The broad priorities echo the agency’s CISA 2030 strategy released last month, which calls for using threat intelligence and analyzing the potential consequences of disruptions to guide where assistance and investment should go. That strategy also emphasizes protecting industrial technology, improving threat alerts and coordinating more closely with intelligence agencies and infrastructure operators.
The agency will roll out additional guidance in the coming months to help divisions across the cyberdefense shop adopt the priorities, Andersen said in the email.
“Publishing our initial CIRs is the starting point of a deliberate, requirements-driven approach to our mission,” he wrote.
Andersen issued the guidance less than a week before President Donald Trump nominated Michael LoSapio, Palantir’s chief information security officer, to lead CISA on Monday. If confirmed, LoSapio would inherit an agency in the midst of rebuilding after cuts over the last two years have reduced its workforce by roughly a third. The agency has been without a Senate-confirmed director since January 2025 when Trump retook office.