Ideas
Vendor lock-in finds a new home in AI, and a contract clause won’t fix it
COMMENTARY | GSA’s new AI clause targets vendor lock-in, but enforcement remains a challenge.
Ideas
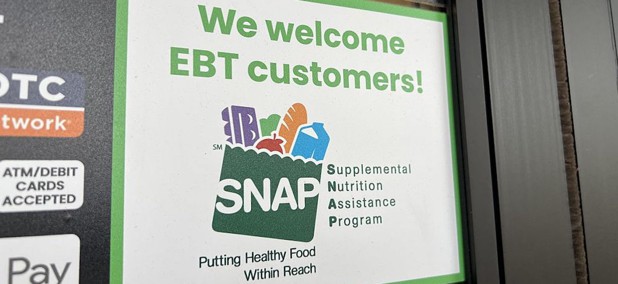
Chip reader technology for SNAP is a worthy investment
COMMENTARY | SNAP card security should be considered as an investment in operational efficiency, dependable access to benefits and program integrity.
Ideas
Congress is already paying for loan systems. It should pay for one.
COMMENTARY | A shared lending platform could save hundreds of millions of dollars annually, reduce fraud and speed up federal loans.
Ideas
The Fed's 35-year open data bet is a model for the AI era
COMMENTARY | Half of FRED's friends are now computers. The St. Louis Fed's response offers a playbook for every agency that publishes data.
Ideas
Building the foundation for autonomous operations
COMMENTARY | In an autonomous enterprise, people and intelligent agents work together inside connected processes.
Ideas
FAFSA's turnaround wasn't a miracle. That's the point.
COMMENTARY | Paying for their education should not depend on whether a system failed badly enough to get fixed in the first place.
Ideas
Cyber recovery deters what no kill switch can stop
COMMENTARY | A kill switch is a last resort, not a control system or option to use daily.
Ideas
The internet of (compromised) things: securing IoT when you can’t trust (any) “thing”
COMMENTARY | Is industrial IoT really more secure than the IoT devices we have in our homes?


Ideas
On 9/11’s 25th anniversary, modernizing government starts with remembering our past
COMMENTARY: Reflecting on 9/11 Commission-driven information sharing structural reforms
Ideas
The quantum security deadline just got harder to ignore
COMMENTARY | Quantum security is a national defense priority, not a future planning exercise.
Ideas
Compliance theater is over: What FedRAMP 20x means for every vendor selling to government
COMMENTARY | Attacks now move faster than human-paced patch cycles can keep up with and a compliance program built around periodic reviews will not catch them.
Ideas
Closing federal security gaps in an era of AI-enabled attacks
COMMENTARY | Agencies that align IT, security, data and AI leadership can be prepared for the speed and scale of tomorrow’s AI threats.
Ideas
CMMC Works. Now let’s sharpen it.
COMMENTARY | This is not the moment to loosen the standard. The Defense Federal Acquisition Regulation Supplement requirements behind CMMC should not change.
Ideas
Gartner has confirmed the battle for authority is happening right now. Is your agency ready for the aftermath?
COMMENTARY | If agencies don't act, the consequences won't be abstract.
Ideas
CISA just changed the rules. Is your vulnerability program ready?
COMMENTARY | BOD 26-04 is a mandate about process. What it implies is a mandate about intelligence.
Ideas
3 security questions agencies should answer before Gold Eagle lands
COMMENTARY | The agencies that build that capability will define what good looks like for the next decade.
Ideas
The agentic SOC for today’s air-gapped environments: rethinking cyber defense in the age of AI
COMMENTARY | If you're not using AI to defend against AI, then the adversary has already closed the gap.
Ideas
The perimeter is gone. Security has to follow the data.
COMMENTARY | Many zero trust plans are still anchored to the old idea of the border. That protects a version of government IT that no longer exists.
Ideas
Modernization redefined: Why public sector IT leaders must put data at the center of AI architecture
COMMENTARY | Public sector organizations must put data first when making infrastructure choices.
Ideas