CISA vulnerability response chief departing agency after nearly six years
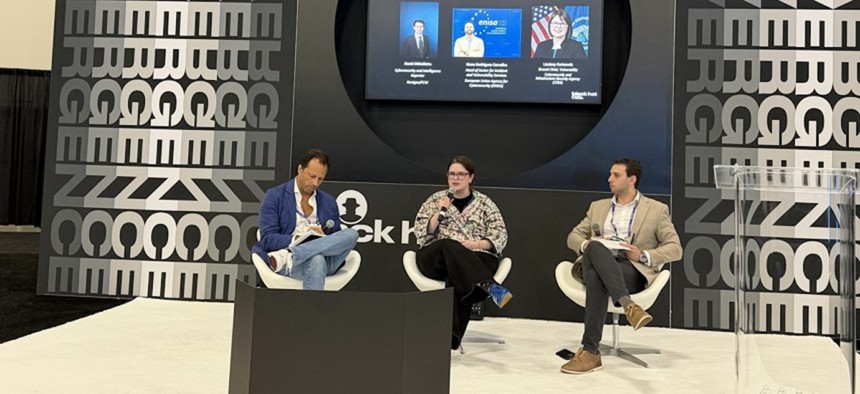
(L to R) Nuno Rodrigues Carvalho, head of sector for Incident and Vulnerability Services at the European Union Agency for Cybersecurity, and Lindsey Cerkovnik, branch chief of vulnerability response and coordination at the Cybersecurity and Infrastructure Security Agency, speak with Nextgov/FCW Cybersecurity Reporter David DiMolfetta Aug. 6 at the Black Hat cybersecurity conference. David DiMolfetta/Staff
Lindsey Cerkovnik helped oversee agency efforts to track software flaws. She plans to start a new role in November.
Lindsey Cerkovnik, a senior Cybersecurity and Infrastructure Security Agency official whose office helps oversee a key global system for tracking software vulnerabilities, is leaving government service this week after nearly six years at the agency.
Cerkovnik, CISA’s branch chief for vulnerability response and coordination, announced her departure in a LinkedIn post. She said she would begin a new role in mid-November.
In a message to Nextgov/FCW, she declined to comment on her next position for the time being. It was not immediately clear who would take over her responsibilities at the cyber agency.
The exit is significant because it comes amid global discussions over how to sustain a bedrock vulnerability-tracking program Cerkovnik’s office helps oversee. Last year’s near-expiration of the federal contract supporting this framework, known as the Common Vulnerabilities and Exposures Program, highlighted how heavily a resource used by governments and businesses worldwide depended on continued U.S. support.
CISA extended the contract, averting a possible interruption in data flows, but the episode spurred calls for firmer congressional backing as AI-assisted research increases the volume of flaws organizations must assess and address.
CVE assigns standardized identifiers to software flaws so researchers, vendors and governments can track the same problems. It’s used by virtually all cyber practitioners, ranging from software developers in the private sector to analysts inside national intelligence agencies.
At an August panel during the Black Hat cybersecurity conference moderated by Nextgov/FCW, Cerkovnik said the CVE program could keep up as researchers discover more software flaws. But the harder task, she said, would be helping organizations distinguish weaknesses that pose a serious threat from those that are less urgent to fix.
“Not all vulnerabilities matter at the same level,” she said. She also supported giving CVE a formal basis in federal law but cautioned against rigid rules that could hinder its response to emerging cyber threats.
Cerkovnik joined CISA in May 2021 to lead vulnerability management for industrial control systems, the technology used to operate equipment in factories, utilities and other critical infrastructure. She became branch chief in May 2023 after serving as acting chief of the agency’s vulnerability response and disclosure section, according to her LinkedIn profile.
Before CISA, she spent more than four years at Idaho National Laboratory, working on control systems cybersecurity and cyber investigations.
Her work has involved programs that help agencies and businesses identify security weaknesses, share information about them and decide which need urgent repairs. In her post, she highlighted the agency’s response to Log4Shell, the launch of a coordinated vulnerability disclosure platform and work on the Known Exploited Vulnerabilities catalog.
That catalog identifies flaws that hackers have already exploited, helping organizations prioritize fixes.
Cerkovnik’s departure also comes as artificial intelligence-assisted vulnerability research puts new pressure on efforts to clamp down on digital security flaws before hackers can exploit them. This week, CISA joined the NSA and FBI in urging organizations to fix critical flaws in PHP, widely used software that helps run websites worldwide.