
ShinyHunters claims FBI data theft, demands bureau retract cyber warning
Anna Moneymaker/Getty Images
The hacking group says it obtained sensitive employee and applicant records. The full scope of the claimed breach remains unclear.
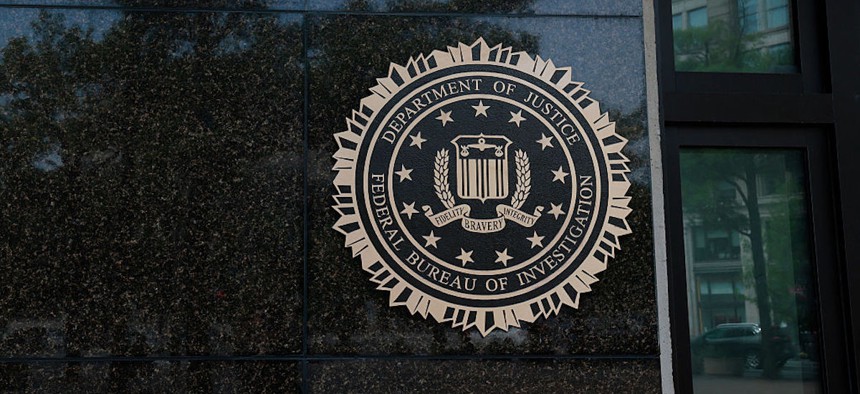
The ShinyHunters cybercriminal group claims it has stolen sensitive information about FBI employees and job applicants and is demanding that the bureau retract a public warning about its tactics within a week.
The demand, addressed to FBI Director Kash Patel and Cyber Division Assistant Director Brett Leatherman, seeks to pressure the agency into changing its public account of the group’s activities. The group claims the effort was not financially motivated.
In a statement attributed to the group, the hackers claimed access to several FBI services, including human resources systems and a service identified as Medlink.
“We have compromised the FBI. We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI for a job,” the statement says.
An FBI jobs page also displayed a “Scheduled Maintenance Underway” notice Tuesday, saying the site was temporarily unavailable. The notice did not identify a security incident or explain whether the outage was related to the hackers’ claims. An earlier version of the webpage appears to show a seizure notice posted by the group.
The language ShinyHunters wants removed appears in a May 15 FBI public service announcement issued after an attack disrupted an online learning management system used by educational institutions.
In the announcement, the FBI warned that ShinyHunters uses harassment to pressure victims, including threatening communications to victims and family members and, in some cases, swatting, the practice of calling in false emergency reports intended to trigger an armed police response at someone’s home. The alert also warned that attackers may exaggerate their access to personal information or falsely claim to possess compromising photographs or videos.
ShinyHunters denied those practices in its statement and gave the bureau one week to correct or remove the warning.
An FBI spokesperson did not immediately return a phone call or an email requesting comment on the demands. Nextgov/FCW has also reached out to the FBI Agents Association, which advocates on behalf of active and retired FBI special agents.
If the claimed employee records are authentic, their exposure could give criminals or foreign intelligence services information useful for identifying, contacting or intimidating FBI personnel and their families.
The claims come as the FBI works to pursue a more coordinated campaign focused on dismantling hackers’ infrastructure and arresting cybercrime operatives. Its new cyber strategy released this month in part emphasizes disrupting criminal hackers even when those responsible remain beyond the immediate reach of U.S. law enforcement.
404 Media reported earlier Tuesday that a ShinyHunters representative provided the news outlet a file appearing to contain information on roughly 5,000 FBI employees, including names, addresses, phone numbers, birth dates and, in some cases, details about their spouses.
A representative told the outlet that the hackers gained access Monday night through what they described as a previously unknown vulnerability in Oracle’s PeopleSoft software, then accessed servers in Amazon Web Services’ GovCloud environment. The representative claimed the group took between two and three terabytes of data.
The account of the intrusion has not been independently verified. Nextgov/FCW has asked Oracle and AWS for comment.
David DiMolfetta can be reached on Signal via username djd.99
NEXT STORY: AI agents are getting better at cybersecurity. That cuts both ways.