CISA
Officials see gaps in election communications as AI makes foreign influence easier
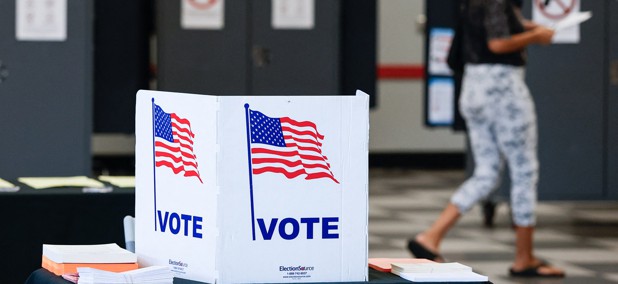
Sources describe weakening cooperation between the federal government and state and industry partners ahead of the midterms, as AI gives foreign operatives cheaper ways to produce and spread deceptive messages.
FBI seizes websites supporting Chinese contractor’s hacking operations
U.S. agencies targeted tools used to find security weaknesses and break into networks, warning of threats to critical infrastructure.
Renewed CISA support comes too late for midterm prep, some election officials say
Arizona still plans to accept federal help on Election Day, while officials warn that staffing cuts have weakened relationships and left smaller jurisdictions with fewer resources.
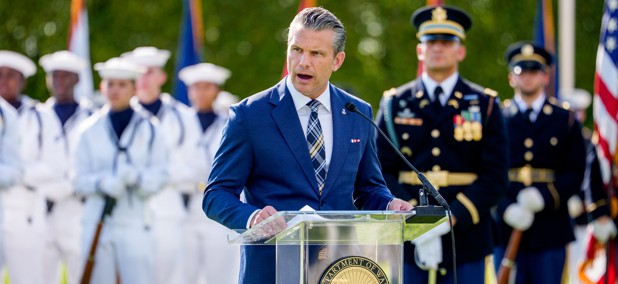
Hegseth orders cyber, intelligence agencies to prioritize election defense
The directive comes as the administration has dismantled or reorganized offices that tracked foreign influence and reduced civilian election security support.
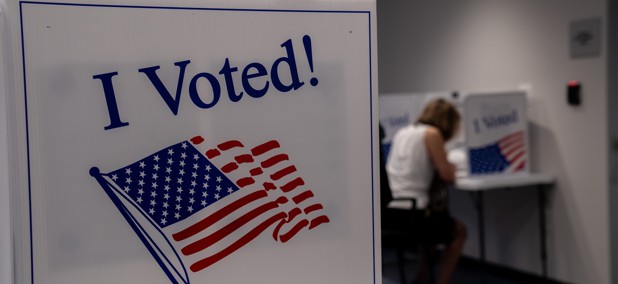
CISA pledges election security support after cuts weakened ties with states
A new plan emphasizes threat sharing and coordination ahead of the midterms, but does not explain how those commitments fit with proposed cuts to dedicated election security funding.
CISA has roughly 250 prospective hires awaiting clearance, agency chief says
Acting Director Nick Andersen says the agency is prioritizing operational teams and regional staff as it works to rebuild its workforce after reductions last year.
Former CISA employee pleads guilty to defrauding government with secret contractor jobs
Prosecutors say Richeline Fung secretly held contractor jobs tied to six agencies and claimed up to 33-hour workdays while working full time for the federal cyber agency.
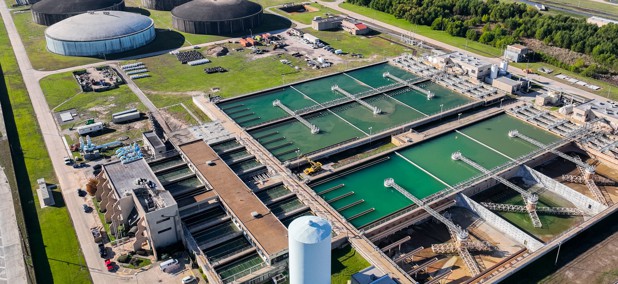
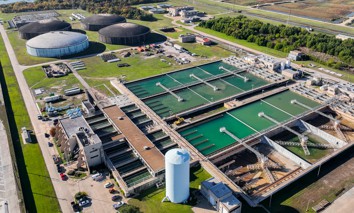
White House launches water cybersecurity pilot in Texas
Project Watershed 250 will stress-test utilities over six months and could serve as a model for protecting water providers nationwide.
Exclusive
House Democrats ask GAO to review CISA workforce cuts
Lawmakers want Congress’ watchdog to assess what capabilities were lost after the cyber agency shed roughly one-third of its staff.
CISA contemplates whether to hire security software buying help
The Cybersecurity and Infrastructure Security Agency issued a sources sought notice that describes its desire to bring in a company that can help manage enterprise license and materials purchases.
CISA just changed the rules. Is your vulnerability program ready?
COMMENTARY | BOD 26-04 is a mandate about process. What it implies is a mandate about intelligence.
CISA cautions against rigid rules for future of cyber vulnerability program
A top agency official said formal backing from Congress could strengthen the global vulnerability-tracking system but warned against measures that may limit its ability to adapt to ever-changing hacking threats.
Exclusive
CISA still finds water system controls exposed online amid multistate hacks
The agency is working with the FBI to help victims but is not attributing the cyber intrusions to any group, acting director Nick Andersen told Nextgov/FCW.
Cyber industry coalition urges federal action after suspected Iran-linked water hacks
The group called on CISA to impose baseline security standards across federal operational technology systems and pressed Congress to revive several stalled cyber initiatives.
CISA urges water utilities to take exposed systems down after Minnesota hacks
A memo distributed to water industry members and obtained by Nextgov/FCW makes mention of Iran but does not directly present evidence attributing the latest Minnesota incident to the country.
Russian hackers can steal government emails without victims clicking a link, cyber agencies warn
The Russia-linked Laundry Bear group has compromised more than 10 Western organizations through malicious emails that can trigger an exploit when they are viewed or previewed.
CISA expects to finalize key cyber reporting rule by September
Last month, CISA held additional stakeholder town halls on the forthcoming CIRCIA final rule after a now-resolved DHS funding lapse this spring delayed the meetings.
Exclusive
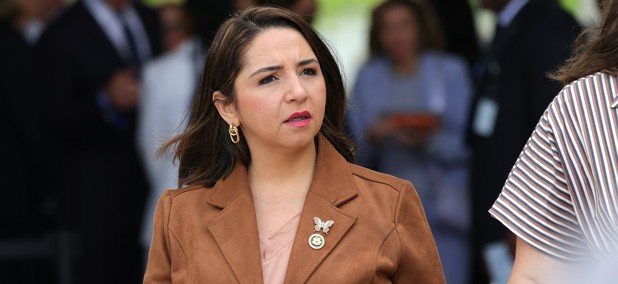
Top House cyber lawmaker plans to introduce DHS overhaul bill by next year
In an interview, Rep. Delia Ramirez, D-Ill., also said she plans to ask officials about how export control measures would affect government agencies’ access to advanced AI models.
Planned NDAA amendment would codify CISA’s role in cyber vulnerability program
The measure, expected as a proposed add-on to the government’s 2027 defense package, targets a bedrock cybersecurity vulnerability-tracking system after a contracting fiasco last year.
Exclusive
CISA now has full Mythos Preview access, people familiar say
The cyberdefense agency received access around a week ago, but the White House has not yet set clear parameters for how the agency should use the model.