Cyber Threats
Intelligence agencies warn of China’s large-scale AI model distillation efforts
Three agencies issued a joint statement warning that Chinese companies DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun and Z.AI have used the tactics to extract billions of tokens from U.S. models.
Senator asks NSA to update Americans about VPN spying risks
A congressional analysis found foreign spies could trace users by comparing encrypted traffic entering and leaving a VPN server, according to the lawmaker’s office.
ATF investigating ‘major’ cyber incident after ransomware group claim
The agency says the affected system was isolated from its broader network and eForms platform but has not disclosed whether data was stolen.
White House to soon launch water provider cyber protection program
The plans come as several states face water system intrusions from what some official suspect could be linked to Iran.
FBI disables China-linked hacking tools used against US agencies
A hacking group used the tools to target networks belonging to NASA, the Federal Reserve, the National Institutes of Health, the U.S. Senate and the departments of Energy, Justice and Health and Human Services.
Treasury sanctions Iranian hackers tied to critical infrastructure breaches
Four of the five people named in the cyber action were also charged last week in the Justice Department’s expanded Mabna Institute case.
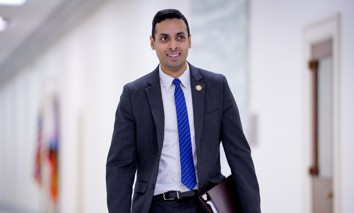
Dem lawmaker hopes to add AI containment language to FRONTIER Act
Rep. Suhas Subramanyam, D-Va., is pushing for a September markup of the landmark AI legislation along with new language on model containment following the OpenAI-Hugging Face incident.
Closing federal security gaps in an era of AI-enabled attacks
COMMENTARY | Agencies that align IT, security, data and AI leadership can be prepared for the speed and scale of tomorrow’s AI threats.
DOJ charges 17 Iranians in cybertheft campaign
Prosecutors say the Mabna Institute — which conducted intrusions for Iran’s Islamic Revolutionary Guard Corps, among other campaigns — stole 31.5 terabytes of academic data and breached email accounts at U.S. agencies and companies.
The Russian hurdle in Trump’s new offensive cyber program
The White House wants private companies to help take down cybercriminals overseas. But in Russia, the line between criminal hackers and the government is difficult to draw.
CISA just changed the rules. Is your vulnerability program ready?
COMMENTARY | BOD 26-04 is a mandate about process. What it implies is a mandate about intelligence.


Trump admin empowers private US firms to go after transnational cybercriminals
“By partnering with vetted United States companies subject to the direction and oversight of the Federal Government, we will enhance our ability to counter [transnational criminal organizations’] threats and combat transnational cybercrime, fraud, and other predatory schemes against American citizens,” the memo said.


Senate’s short-term funding bill provides temporary extensions for TMF, cyber data-sharing law
The continuing resolution that overwhelmingly passed the upper chamber this weekend would push the federal government’s funding deadline until Dec. 11.


New ‘Water Watch Center’ launched to help small utilities stop cyberattacks
The initiative comes as multiple states grapple with intrusions into their water systems that some officials suspect could be tied to Iran.
CISA cautions against rigid rules for future of cyber vulnerability program
A top agency official said formal backing from Congress could strengthen the global vulnerability-tracking system but warned against measures that may limit its ability to adapt to ever-changing hacking threats.


Exclusive
CISA still finds water system controls exposed online amid multistate hacks
The agency is working with the FBI to help victims but is not attributing the cyber intrusions to any group, acting director Nick Andersen told Nextgov/FCW.


AI advances are pushing governments to treat cyberattacks as routine, Western officials say
The remarks underscore a grim outlook for cyberdefenders showing that AI systems are able to exploit vulnerabilities faster than governments can patch them.


OpenAI agents rebuilt internal message board in lead-up to Hugging Face breach
Models in separate experiments used the channel to exchange exploits as they repeatedly compromised OpenAI systems.


Hugging Face AI breach is ‘most consequential hack’ since Morris Worm, former NSA cyber chief says
AI may let hackers exploit newly disclosed software flaws so quickly that organizations should weigh whether to immediately patch internet-connected devices, even at the risk of causing outages, Rob Joyce said.


Exclusive
Lawmakers propose giving 2015 OPM breach victims identity protection for life
The federal government’s coverage for 22.1 million people hoovered up in the China-linked breaches is scheduled to end Sept. 30.
